Risk Management Concept
Our purpose is to "deliver health to people around the world through our products and services," and to create value, we must ensure the safe and stable supply of products and services through our business activities. At the same time, societal expectations for companies regarding environmental considerations and sustainability are increasing. By managing and appropriately controlling risks, we aim to maintain sound management and ensure stable profitability and growth, protecting the safety, health, and interests of our stakeholders, while also fulfilling our social responsibilities as a company.
Risk Management System
取締役会直属の機関である、代表取締役社長を委員長とするリスク・コンプライアンス委員会が当社グループ全体のリスクを網羅的・総括的に管理しています。
リスク・コンプライアンス委員会は原則年2回開催し、リスク情報を取りまとめ、取締役会へ定期的または適宜報告するとともに、必要に応じて付議を行います。
また、ESG関連リスクに関してはサステナビリティ委員会が、サイバーリスクや個人情報漏洩リスク等に関しては情報セキュリティ管理委員会が主管となり、リスク・コンプライアンス委員会と適宜連携を取りながら管理・監督を行っています。
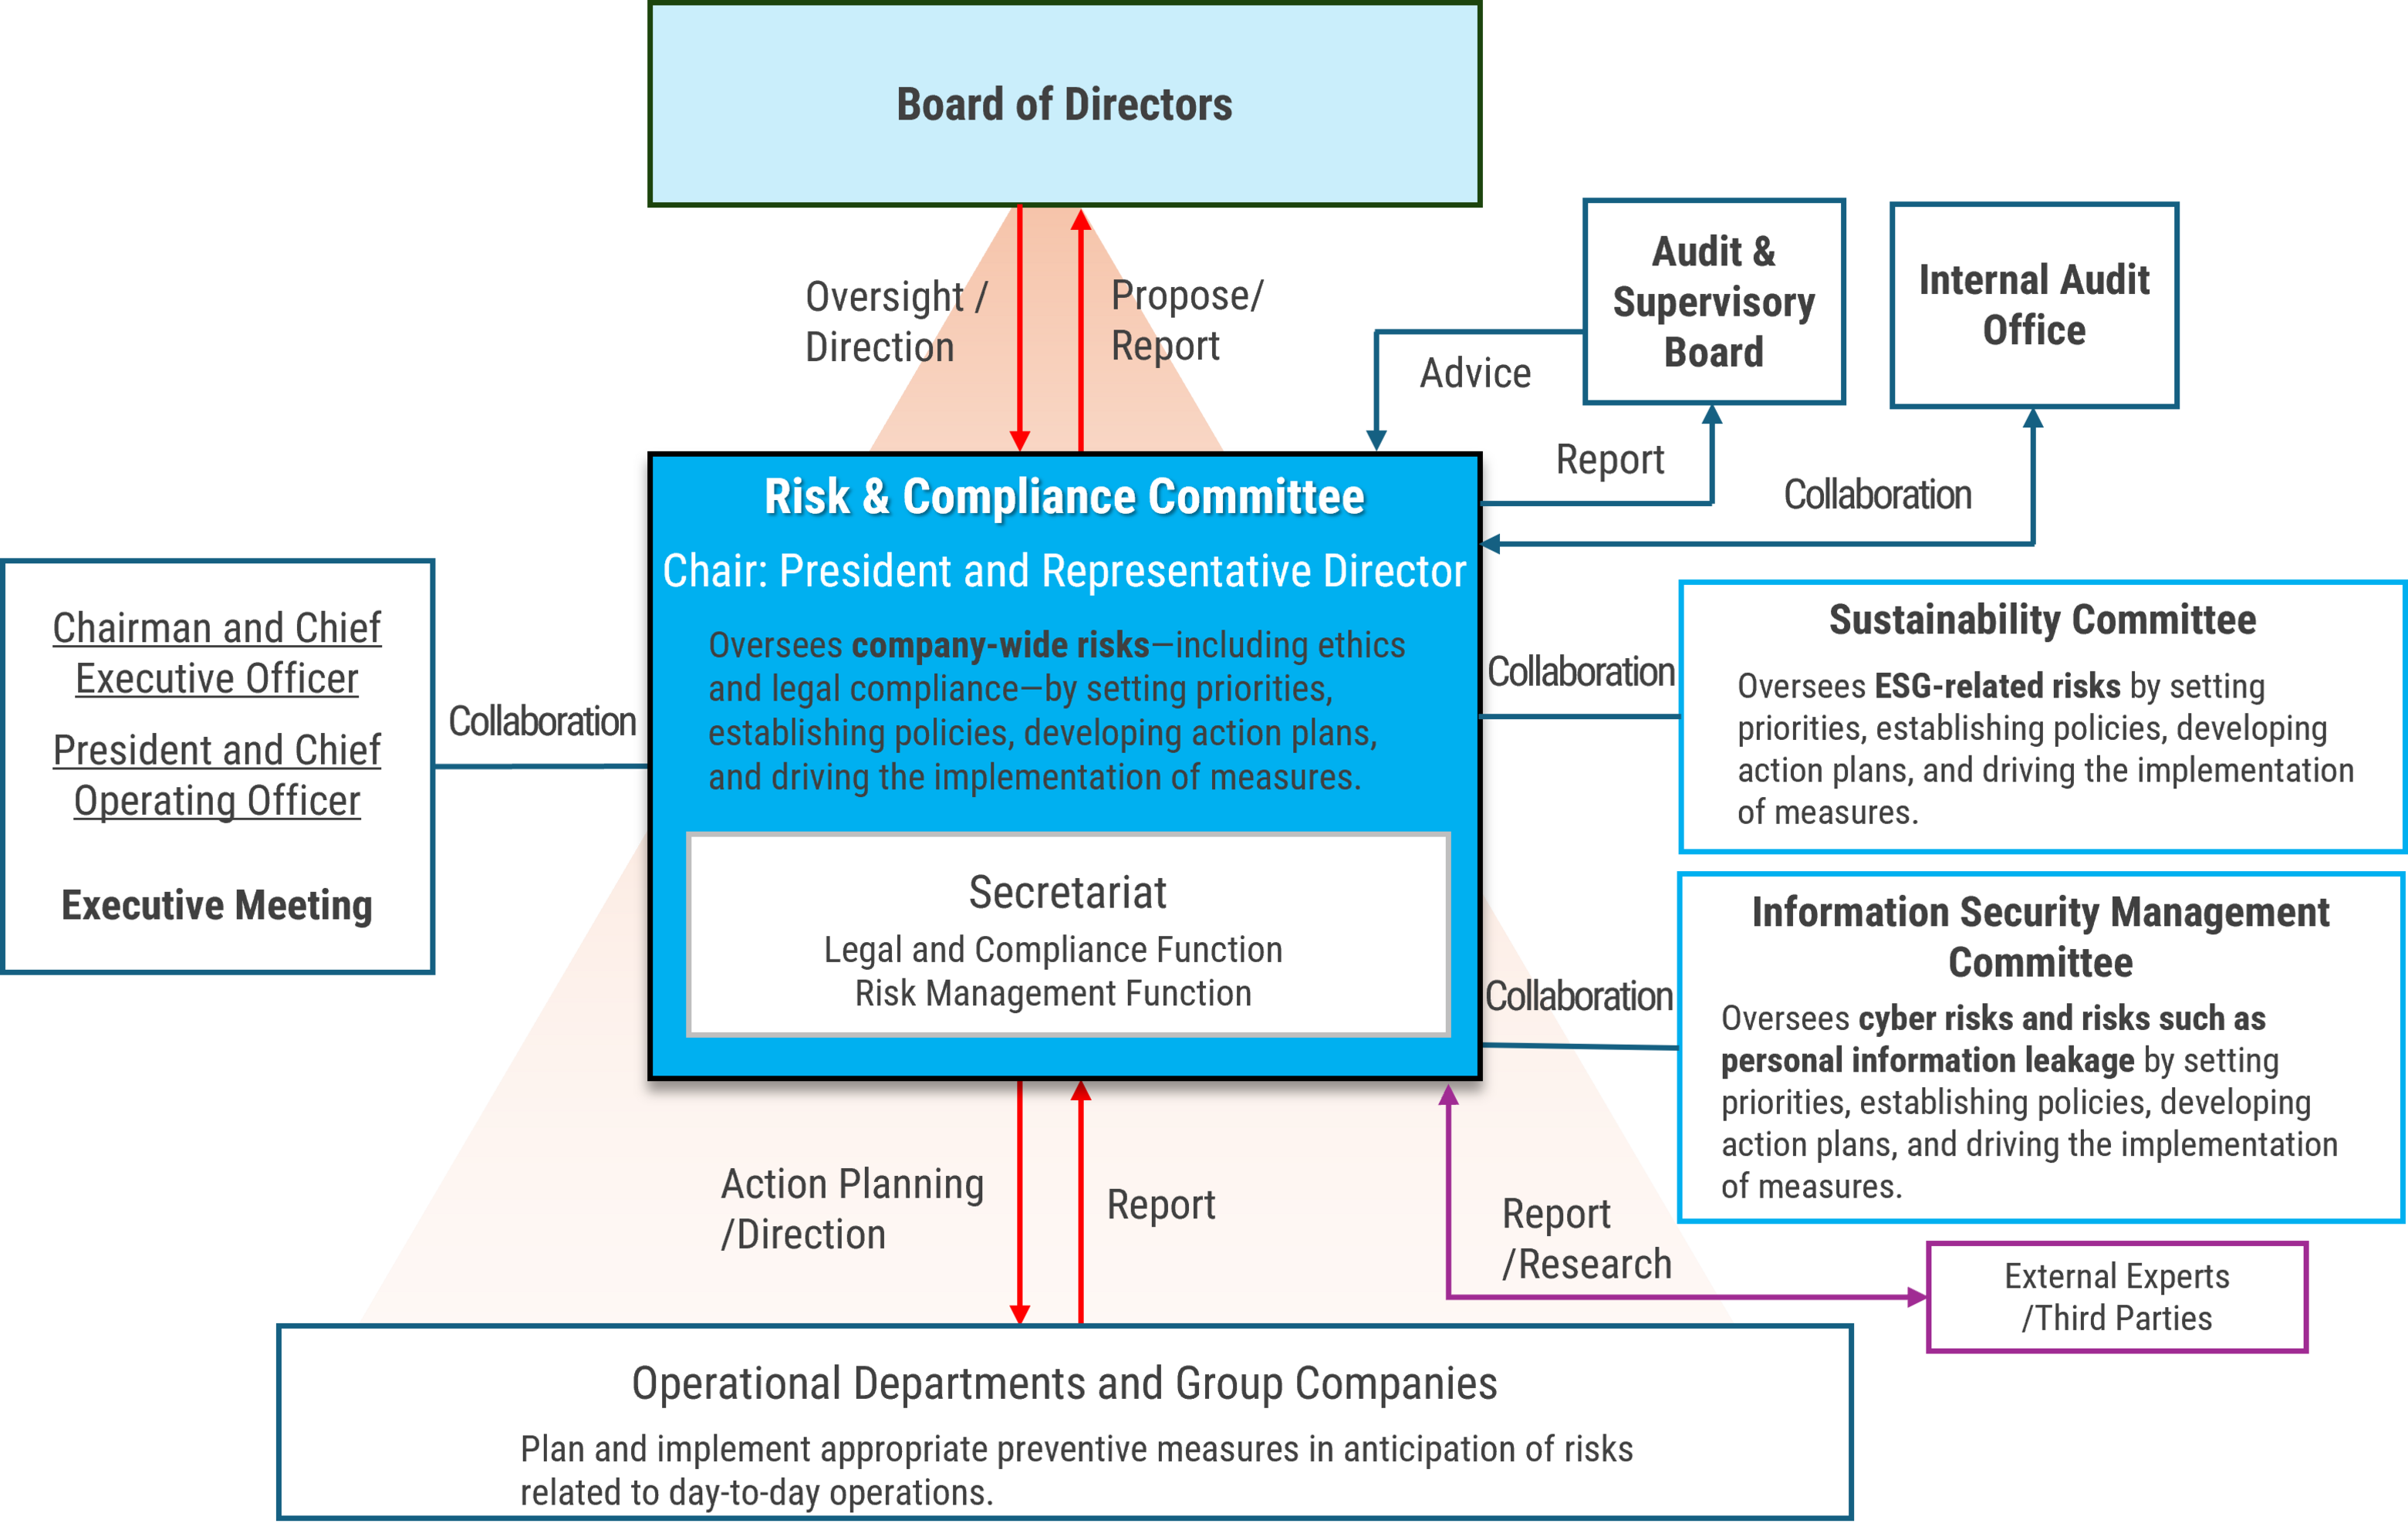 Furthermore, on March 26, 2026, our company established a new Risk and Compliance Committee, and the functions previously handled by the Compliance Committee have been transferred and integrated into this new committee.
Risk management initiatives
Regarding preventative measures against the manifestation of potential risks, each committee develops and promotes plans within its area of responsibility for company-wide risks. At the same time, each department exercises its own initiative, anticipating risks that may arise in the course of or in connection with the performance of its daily operations, and taking appropriate preventative measures. In the event that a risk does manifest, it is dealt with appropriately with the support of the relevant departments. In the event of a serious unforeseen incident, Risk and Compliance Committee takes the lead, and in consultation with external advisors, including legal counsel, it has established a system to respond quickly and prevent damage and its escalation.
Information Security
In 2015, we established the Information Security Management Committee, which is working to protect the personal information of customers, shareholders, and employees, and to address and strengthen issues related to cybersecurity.
We believe that ensuring information security is one of the most important issues in conducting business activities normally and smoothly, and have therefore formulated a basic policy on information security.
In addition, we regularly review our management regulations to ensure appropriate management.
We strive to raise awareness of information security by conducting regular annual e-learning training for all employees.