Risk Management Concept
Our purpose is to "deliver health to people around the world through our products and services," and to create value, we must ensure the safe and stable supply of products and services through our business activities. At the same time, societal expectations for companies regarding environmental considerations and sustainability are increasing. By managing and appropriately controlling risks, we aim to maintain sound management and ensure stable profitability and growth, protecting the safety, health, and interests of our stakeholders, while also fulfilling our social responsibilities as a company.
Risk Management System
Risk and Compliance Committee, chaired by President and Representative Director and a body directly under the Board of Directors, comprehensively and holistically manages risks across the entire group. Risk and Compliance Committee meets twice a year in principle to compile risk information and report it to the Board of Directors regularly or as needed, and submits it for deliberation as necessary. In addition, the Sustainability Committee is responsible for ESG-related risks, and the Information Security Management Committee is responsible for cyber risks and personal information leakage risks, etc., and they manage and supervise these risks in cooperation with Risk and Compliance Committee as appropriate.
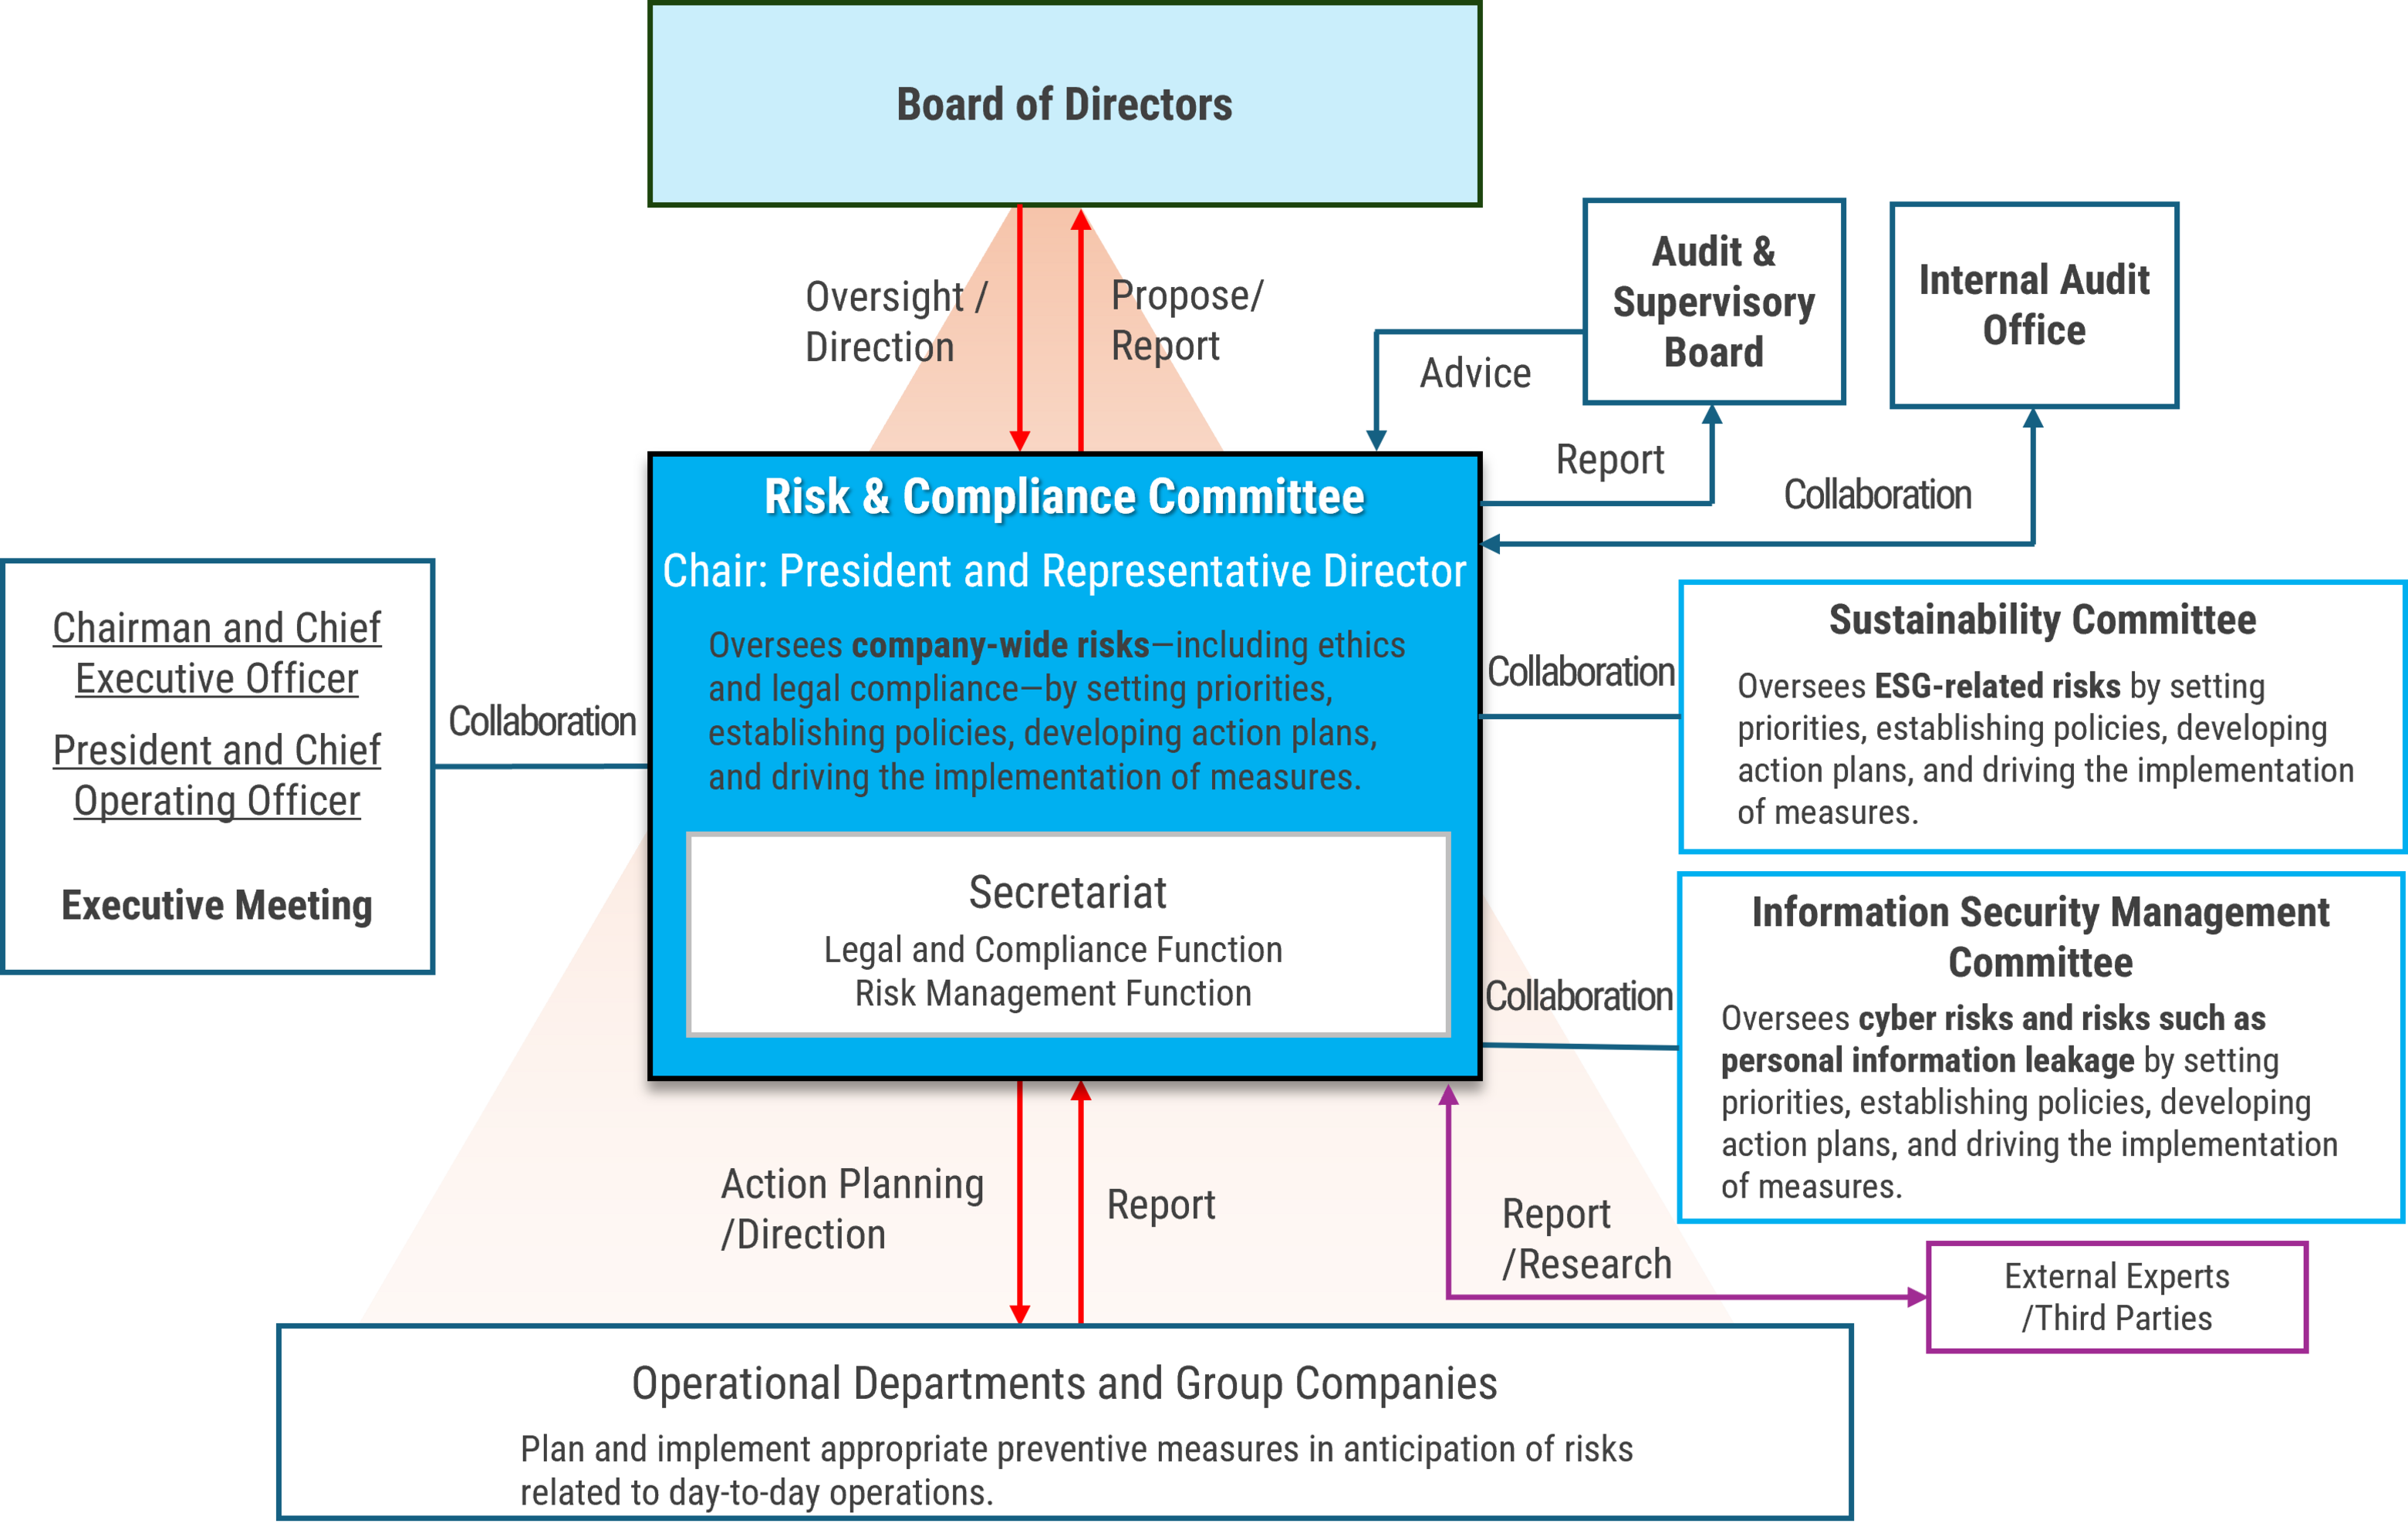 Furthermore, on March 26, 2026, our company established a new Risk and Compliance Committee, and the functions previously handled by the Compliance Committee have been transferred and integrated into this new committee.
Risk management initiatives
Regarding preventative measures against the manifestation of potential risks, each committee develops and promotes plans within its area of responsibility for company-wide risks. At the same time, each department exercises its own initiative, anticipating risks that may arise in the course of or in connection with the performance of its daily operations, and taking appropriate preventative measures. In the event that a risk does manifest, it is dealt with appropriately with the support of the relevant departments. In the event of a serious unforeseen incident, Risk and Compliance Committee takes the lead, and in consultation with external advisors, including legal counsel, it has established a system to respond quickly and prevent damage and its escalation.
Information Security
Since 2015, we have established an Information Security Management Committee to address and strengthen the protection of personal information of our customers, shareholders, and employees, as well as to tackle cybersecurity challenges. The Chief Information Officer (CIO) serves as the chairperson of this committee.
We believe that ensuring information security is one of the important issues for conducting business activities normally and smoothly, and therefore we have formulated an information security basic policy.
Furthermore, we ensure proper management by regularly reviewing our management regulations.
We strive to improve information security awareness by regularly conducting e-learning training for all employees every year and by familiarizing them with the reporting and response processes in the event of an incident.